
Vulnerability Assessment
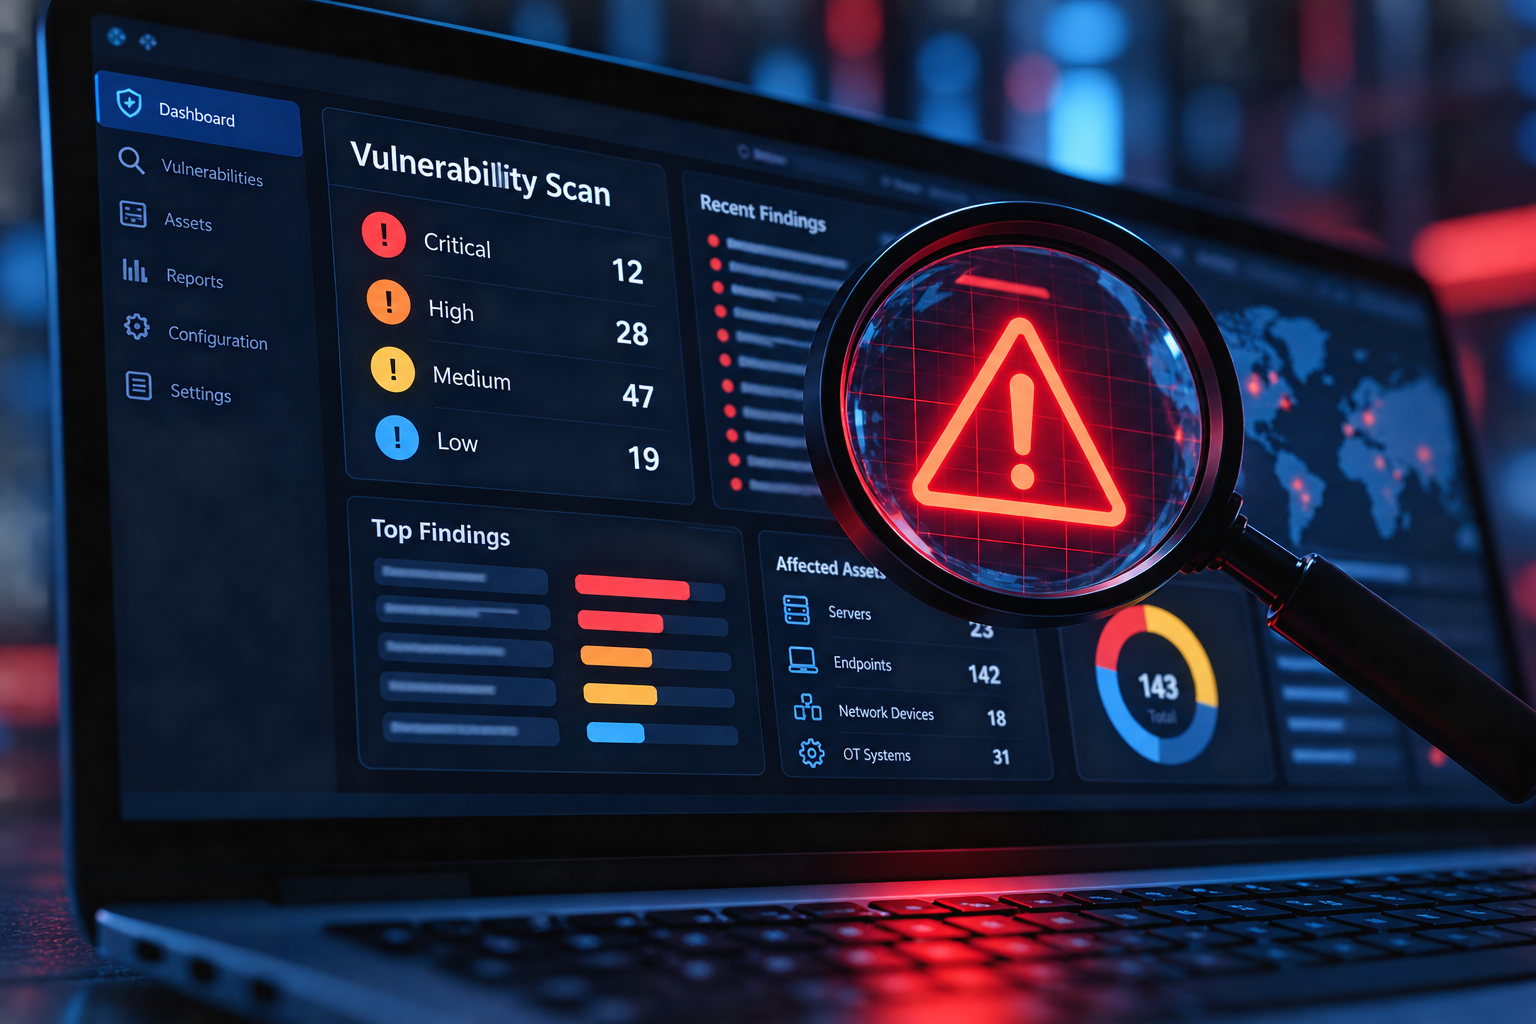
Vulnerabilities can exist anywhere within an organization’s technology environment, including operating systems, applications, network devices, security appliances, and system configurations. 227 InfoSec conducts comprehensive vulnerability assessments to identify known vulnerabilities, insecure configurations, outdated software, and weaknesses that could increase the likelihood of compromise. Findings are evaluated and prioritized based on severity and potential impact, giving your organization a clear understanding of where security improvements are needed.
Our assessments combine automated vulnerability scanning with expert analysis to provide more than a list of scanner results. 227 InfoSec reviews identified vulnerabilities, validates findings where appropriate, evaluates security configurations and baselines, and develops actionable recommendations for remediation. Assessments can be conducted as a point-in-time evaluation or as part of an ongoing vulnerability management program to track remediation, identify emerging vulnerabilities, and continuously reduce organizational risk.