
Cybersecurity Assessments (33 CFR 101.650)
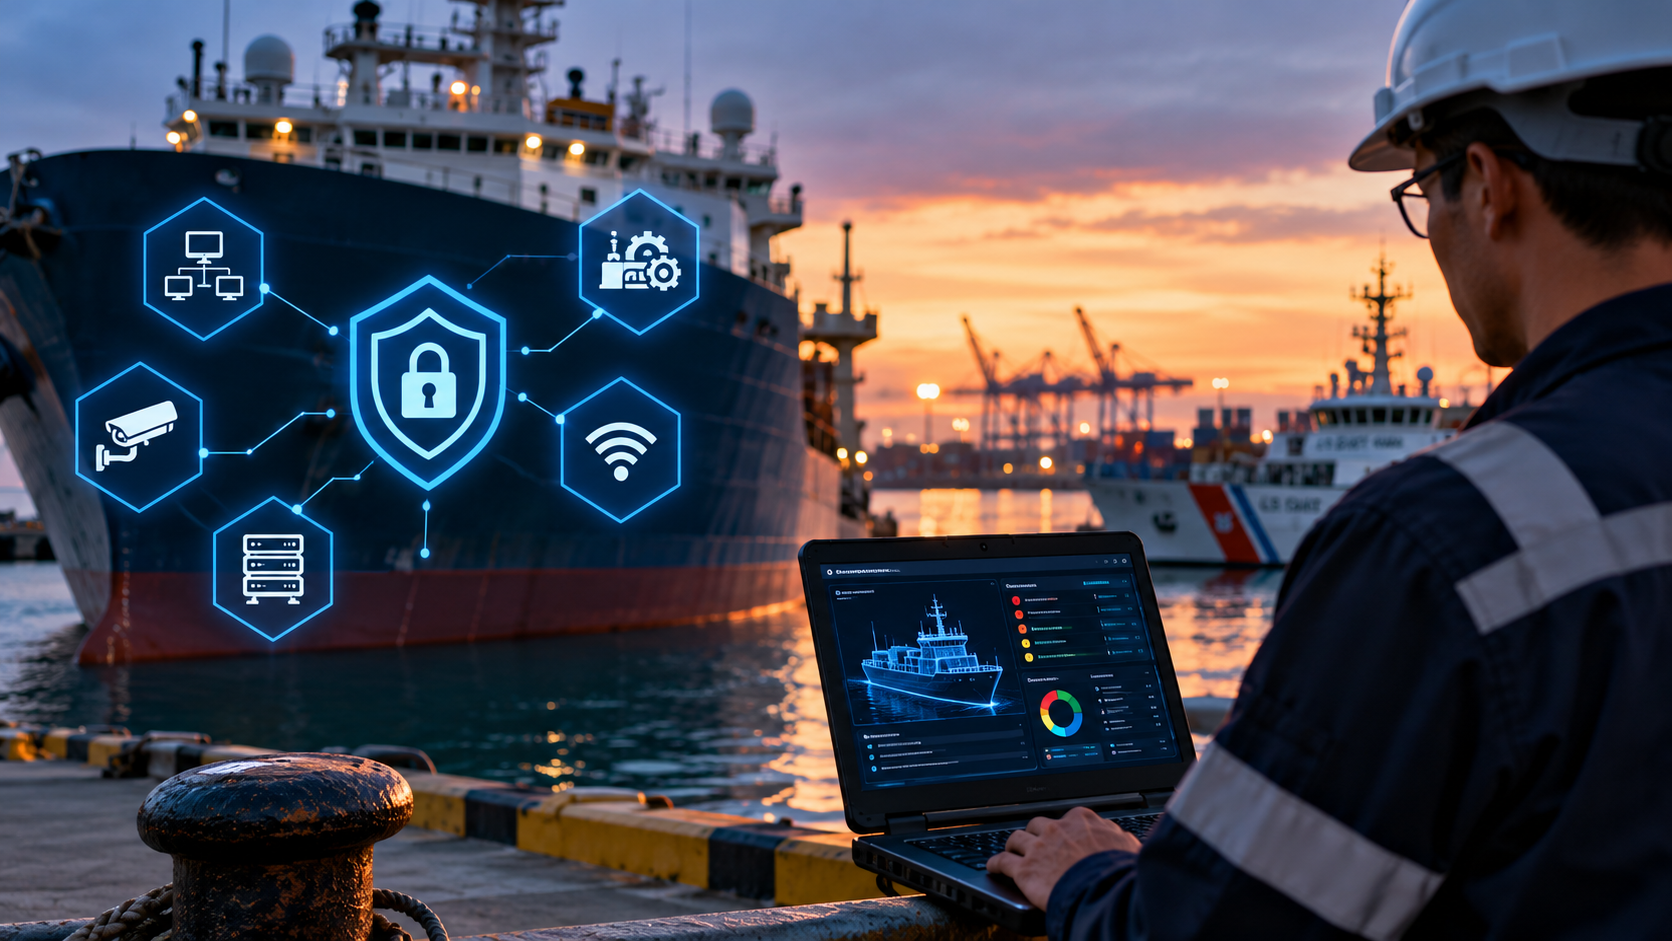
227 InfoSec conducts vessel and facility Cybersecurity Assessments (CSAs) aligned with 33 CFR Part 101, Subpart F and current U.S. Coast Guard guidance. Our assessments evaluate the IT and OT systems supporting maritime operations to identify cybersecurity vulnerabilities, operational dependencies, critical systems, existing safeguards, and conditions that could increase the risk of operational disruption or a Transportation Security Incident (TSI).
Our assessment methodology combines document and architecture review, personnel interviews, physical inspection, system observation, and risk analysis to evaluate cybersecurity controls without unnecessarily disrupting vessel or facility operations. Findings are documented with risk-based recommendations and corrective actions to support Cybersecurity Plan (CSP) development and maintenance, identify required compensating controls, and provide a defensible record of cybersecurity risks and their disposition.